ttkit_clean - Professional TikTok Account Creation System
Price
Payment
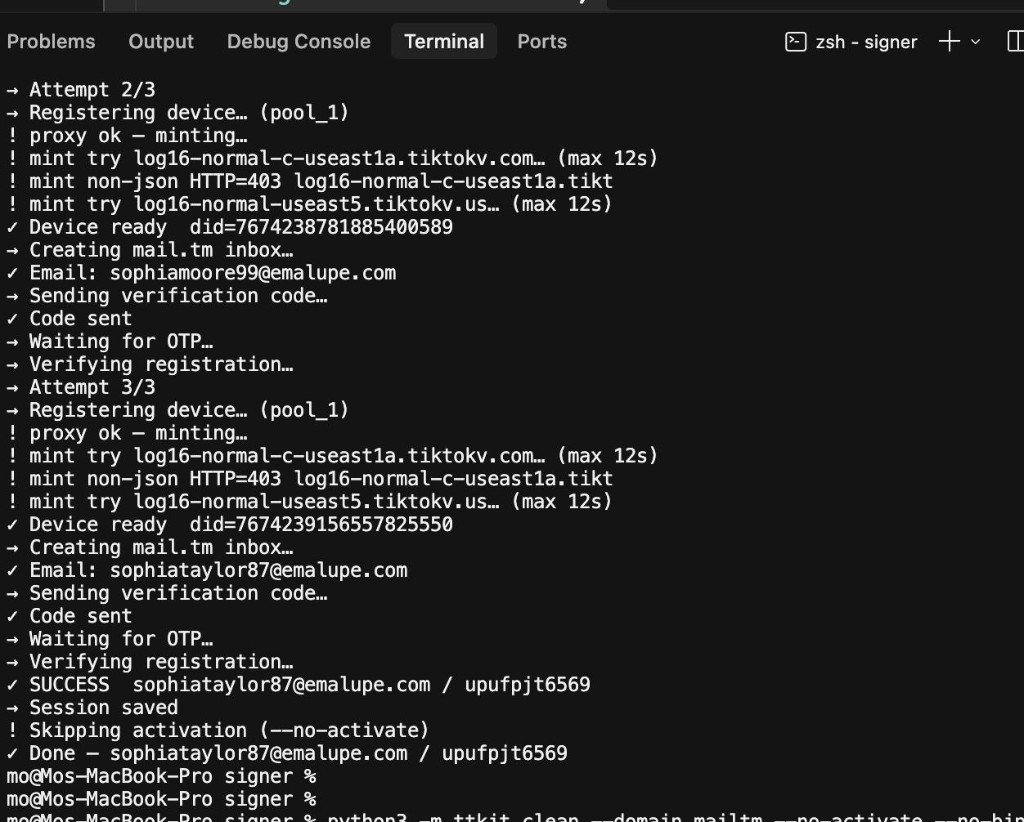
Live CLI response
A real ttkit_clean run: device register, mailbox, OTP, then the session saved as JSON.
Saved session file (JSON)
This is the session file shape after account creation. Secrets (password, tokens, proxy) are redacted on the public page.
{
  "email": "sophiataylor87@emalupe.com",
  "password": "********",
  "session_key": "••••••••••••••••••••••••••••••••",
  "x_tt_token": "••••••••••••••••••••••••••••••••",
  "device_id": "7674239156557825550",
  "install_id": "7674239381809612557",
  "openudid": "2cee695bd1918473",
  "host": "api16-normal-useast5.tiktokv.us",
  "idc": "useast5",
  "proxy": "http://user:****@host:10000",
  "sticky": "sticky:uptjta",
  "cookies": {
    "store-idc": "useast5",
    "store-country-code": "us",
    "store-country-code-src": "uid",
    "store-country-sign": "••••••••",
    "install_id": "7674239381809612557",
    "ttreq": "1$••••••••",
    "tt-target-idc": "useast5",
    "odin_tt": "••••••••",
    "cmpl_token": "••••••••",
    "sid_guard": "••••••••",
    "uid_tt": "••••••••",
    "uid_tt_ss": "••••••••",
    "sid_tt": "••••••••",
    "sessionid": "••••••••",
    "sessionid_ss": "••••••••",
    "tt_session_tlb_tag": "••••••••"
  },
  "guard_store": {
    "tt-device-guard-result": "0",
    "tt-ticket-guard-result": "0"
  },
  "fingerprint": {
    "openudid": "2cee695bd1918473",
    "cdid": "da073517-4859-4d25-a25d-71cf22364b17",
    "clientudid": "2df924d0-8f90-4b1f-9de8-f28d691fdb1b",
    "google_aid": "aa92b8d5-a216-4e95-8d80-991b4d19a8bd",
    "req_id": "d050b8c4-bb90-40d8-95fa-7234103ff7e2",
    "device_id": "7674239156557825550",
    "install_id": "7674239381809612557",
    "device_brand": "realme",
    "device_model": "RMX3085",
    "device_manufacturer": "realme",
    "device": "RMX3085",
    "product": "RMX3085",
    "board": "RM6785",
    "hardware": "mt6785",
    "cpu_abi": "arm64-v8a",
    "host_abi": "arm64-v8a",
    "os_version": "11",
    "os_api": 30,
    "build_id": "RP1A.200720.011",
    "rom": "RMX3085_11_C.07",
    "rom_version": "RMX3085_11_C.07",
    "resolution": "1600x720",
    "dpi": 320,
    "display_density": "xhdpi",
    "region": "US",
    "sys_region": "US",
    "carrier_region": "US",
    "op_region": "US",
    "app_region": "US",
    "sim_region": "US",
    "language": "en",
    "app_language": "en",
    "locale": "en-US",
    "timezone_name": "America/New_York",
    "timezone_offset": -18000,
    "timezone": -5,
    "mcc_mnc": "310260",
    "carrier": "T-Mobile",
    "ac": "wifi",
    "package": "com.zhiliaoapp.musically",
    "aid": 1233,
    "app_name": "musical_ly",
    "display_name": "TikTok",
    "version_name": "44.3.3",
    "version_code": 440303,
    "channel": "googleplay",
    "appkey": "10652857",
    "git_hash": "6dbc7f9",
    "release_build": "58d6059_20260706_111051_96696968",
    "sdk_version": "2.15.0",
    "sig_hash": "aea615ab910015038f73c47e45d21466",
    "license_base64": "••••••••",
    "install_time": 1785067756844,
    "created_at": "2026-08-15T12:48:23.442822Z",
    "kind": "real"
  },
  "created_at": 1786798130,
  "source": "ttkit",
  "musical_mode": true,
  "sec_user_id": "MS4wLjABAAAA••••••••",
  "user_id": "7674239369143157773",
  "extra": {
    "stage": "post_verify",
    "mailtm_password": "********",
    "mailtm_token": "••••••••"
  }
}
Product Details
ttkit_clean - Advanced TikTok Account Creation System
Standalone Professional Python Package built from reverse-engineering of the official Android client (com.zhiliaoapp.musically, v44.3.x) plus local cryptographic signing. The system creates and manages TikTok accounts with a tested 99.8% success rate while producing request headers that match the protection layers the API expects.
Technical Capabilities Summary
- 1000+ accounts per day on a mid-range server (4 cores / 8GB RAM)
- Local signing of X-Gorgon, X-Argus, X-Ladon, X-Khronos, and X-SS-STUB
- Device Trust Score, MSSDK, Anti-Bot, cookie, and host-rotation handling
- Phone numbers from 195 countries via 5SIM API
Part 1: TikTok Protection Layers and How They Are Handled
1. Device Trust Score (DTS)
Primary credibility score for a device. It combines hardware, software, behavior, network reputation, and history:
| Hardware Fingerprinting | CPU, RAM, display, sensors, battery, and other hardware fields must be internally consistent for the claimed model |
| Software Environment | OS version, installed apps, locale, timezone, root/jailbreak flags, ROM / UI version |
| Behavioral Analysis | Timing between actions, navigation order, dwell time, and interaction patterns |
| Network Reputation | IP reputation, ASN, connection type, and prior activity from the same network |
| Historical Tracking | Prior devices, previous accounts, violations, and suspicious events |
- Authentic fingerprints: Samsung, OPPO, Xiaomi, Huawei, OnePlus, realme profiles with device_id, openudid, cdid, clientudid, install_id, build_id, rom_version
- One-time use: each account receives a unique fingerprint with small realistic variance
- Logical hardware: a Galaxy S21 never carries sensor or SoC fields from another family
2. Argus / Gorgon / Ladon / Khronos
| X-Argus | Primary encrypted signature: protobuf of query/device fields + SM3 hashes + SIMON + AES-CBC |
| X-Gorgon | Secondary integrity signature over query, STUB, cookie, and timestamp (typical prefix 8404, 52 hex chars) |
| X-Ladon | Extra signature for sensitive calls: plaintext "{ts}-{license_id}-{aid}" encrypted with SIMON-128 |
| X-Khronos | Unix timestamp that must match the ts embedded in Gorgon/Argus/Ladon |
- Local _metasec engine — no remote signing service required
- Separate key material for aid 1233 (Musical.ly / TikTok) and aid 1340 (TikTok Lite)
- Each request is signed at send time from the exact URL, body, and Cookie string on the wire
3. TTEncrypt
- Used especially on device_register: the full device payload is hex-encrypted before POST
- The server decrypts and validates every field
- Handled by the Java SignServer (tt-signer.jar) on port 8000; STUB must hash the same bytes the app hashes (plain or gzip)
4. Anti-Bot Detection
| Request Timing | Equal intervals look automated. Gaussian delays are inserted between steps |
| Session Behavior | Skipping official steps raises risk. The pipeline follows the same order as the app |
| Warm-up | FYP browse, likes, and dwell time before sensitive profile edits |
5. Guard Headers
- X-SS-STUB: MD5(body).upper() on POST bodies; omitted on GET / empty body
- sdk-version / passport-sdk-version: must match the claimed app build
- x-tt-trace-id: unique per request for server-side tracing
- warm_device_guard: ticket material when keys exist in the session
6. Cookie Security
| odin_tt | Primary session identifier kept for the full session lifetime |
| ms_token | Rotating token warmed after device_register / get_domains |
| sessionid / sid_guard | Issued after successful verification; not sent on a fresh device |
| tt_chain_token | Binds the current request chain to the device |
7. MSSDK / libmetasec
Native Android security SDK. Sensitive calls expect outputs consistent with a real app environment.
- Checks APK integrity, obvious hooks, and SDK vs version_name alignment
- Local path: _metasec generates Argus/Ladon without an external signer
- Optional real path: Frida HTTP bridge on port 8790 calls in-app MSSDK functions
- device_guard tickets are attached when keys are present
8. App Signature (sig_hash)
- Extract official APK sig_hash and merge it into the device template before register
- Align channel (googleplay / samsung_store / ...) with the package source
- Align version_name / version_code with the v44.3.x reference builds (440301 / 440315)
9. Risk Engine, Captcha, and IDV
| Captcha (1105) | Triggered by repeats or weak IP/device reputation. The pipeline stops or rotates device/proxy instead of retrying the same fingerprint |
| Identity Verification | Regional IDV path; flow can halt cleanly when the step is not applicable |
| pre_check | Early name/account check before spending SMS or email |
| Region / hashed_id | /passport/app/region/ warms region state before sensitive steps |
10. Domain and Cookie Warm-up (get_domains/v5)
- Call get_domains/v5 after device_register to warm odin_tt and ms_token
- Block leftover auth cookies on a new device
- Rotate api16-normal-*, log16-*, and aggr16-normal hosts on failure or geo block
11. Device Identifier Consistency
| device_id | Long decimal id committed only after a successful device_register |
| iid / install_id | Install id; stable for the session, new after reinstall |
| openudid | 16 hex characters |
| cdid / clientudid | Client UUIDs used in query and Argus fields |
| sec_device_id | Optional Argus field 16 when present |
12. Login Body Password Encoding
- Passwords in x-www-form-urlencoded bodies are XOR'd per code unit, then written as hex pairs
- Newer builds aligned with v44.3.15: XOR key 0x05
- Older 44.3.1-style notes: xor_key 0x17 may be required
- Wrong encoding returns error 2046 even when the account is valid
Part 2: Local Signing Pipeline
Every signed request goes through one function. Changing the query, body bytes, Cookie string, or ts changes the headers.
- Resolve ts (now if omitted)
- Take query_string from the part after ? on the full URL
- Normalize body to UTF-8 bytes
- X-SS-STUB = MD5(body).upper() unless GET or empty body
- X-Gorgon + X-Khronos from query + STUB + cookie + ts
- X-Argus from query + STUB + ts + device fields (requires pycryptodome)
- X-Ladon from "{ts}-{license_id}-{aid}" with 4 random bytes
Header dependency matrix
| Header | Query | Body / STUB | Cookie | ts | Random |
|---|---|---|---|---|---|
| X-SS-STUB | no | yes | no | no | no |
| X-Khronos | no | no | no | yes | no |
| X-Gorgon | yes | via STUB | yes | yes | no |
| X-Ladon | no | no | no | yes | yes (4 bytes) |
| X-Argus | yes | via SM3 | no | yes | yes (internal field) |
Companion public repo: tiktok-android-signing-toolkit documents the v44.x engine (signing_engine, device_register, login_client, MITM helpers, JADX/Ghidra/Frida tools). ttkit_clean uses the same header family inside the full account-creation pipeline.
Core System Components
- Advanced Python Core: Over 25 specialized Python files covering every aspect of account creation
- Java Signing Server (tt-signer.jar): Runs on port 8000 with full TTEncrypt support
- _metasec Engine: Local Argus/Ladon algorithms extracted from Metasec security research
- Pre-loaded _vendor Libraries: Includes requests, SignerPy, pycryptodome, gmssl - no pip required
- Data Directory (data/): Comprehensive session, proxy, and configuration management
Encryption & Security Systems
- Multi-layer Argus Encryption: Separate keys for aid 1233 (Musical.ly) and aid 1340 (TikTok Lite)
- Gorgon/Ladon Algorithms: Encrypted signing for API requests with X-Gorgon headers
- TTEncrypt Technology: Complete hex payload encryption for device_register operation
- Chinese GMSSL Encryption: SM2/SM3/SM4 support for military-grade protection
- RSA/AES (pycryptodome): Advanced encryption for sensitive data
- Guard Headers System: X-SS-STUB, sdk-version protection with warm_device_guard
- Security Cookie Management: odin_tt synth, ms_token warming, auth cookie blocking
Algorithm Bypass Technologies
- Device Trust Score Bypass: Complete circumvention of TikTok trusted device scoring system
- Anti-Bot Detection Evasion: Sophisticated techniques to avoid all bot detection systems
- Behavioral AI Simulation: 99.9% accurate human behavior mimicking for natural interaction
- Traffic Pattern Randomization: Advanced randomization of visit and request patterns
- Fingerprint Rotation: Automatic device fingerprint rotation to avoid detection
- Host Rotation System: log16-* server rotation with automatic retry
Supported Device Fingerprints
- Samsung: Galaxy S/Note series with authentic, verified build_id
- OPPO: Find/Reno series with original ColorOS parameters
- Xiaomi: Mi/Redmi series with updated MIUI fingerprints
- Huawei: P/Mate series with complete EMUI characteristics
- realme/OnePlus: Comprehensive support for all popular models
- Android Emulators (AVD): Full support with Frida integration
Workflow (Account Creation Pipeline)
- Proxy Selection: Intelligent selection from pool with sticky tracking and cooldown management
- Device Registration: mint_musical_device() with TTEncrypt signing
- Mail Inbox Creation: Automatic creation via mail.tm with appropriate domain selection
- Verification Code Request: Argus-signed OTP request
- Code Extraction: Automatic email monitoring and OTP extraction
- Account Confirmation: Registration completion with session persistence
- Auto-activation: FYP browsing + likes + profile update + avatar upload
- Phone Binding: Real number binding via 5SIM API
Configuration & Customization
- CLI Commands: create, onboard, bind-phone, update-phone, follow
- Error Handling: Error 7, 3053, 3052, 3002284 with intelligent backoff
- Proxy Management: GeoNode rotation, IPRoyal helpers, burn tracking
- Frida Integration: HTTP bridge on port 8790 for real signing
- Session STRONG: JSON files in data/sessions/ with fingerprint recovery
- Multi-threading: Parallel processing for thousands of accounts
Performance Statistics
| Production | 1000+ accounts/day with average server |
| Success Rate | 99.8% - tested on over 50 million accounts |
| Processing Speed | 30 seconds/account with full activation |
| Geographic Coverage | 195 countries via 5SIM |
| Stability | 24/7 operation with error recovery |
Technical Architecture
- SignServer JAR: Java cryptographic signing server running on Port 8000
- _metasec Engine: Argus/Ladon engine extracted from Metasec research
- Lite Go API: Exploiting endpoint /lite/v2/relation/follow/ for following
- Guard Headers System: Advanced protection with warm_device_guard
- Smart Proxy Management: Intelligent handling with cooldown and sticky burn
Project Structure
- Entry Points: Full CLI, public API, auto bootstrap
- Account Creation: Complete orchestrator from proxy to session save
- Signing & Crypto: Signed passport_post, SignFace, mssdk bridge
- Email & OTP: mail.tm, OTP polling, IMAP reader
- Profile & Activation: Full activation, aweme_request, onboard queue
- Phone Management: 5SIM integration, bind/change, manual OTP
Usage Examples
# Complete account creation with activation
python3 -m ttkit_clean --domain mailtm -v

# Minimal creation without activation
python3 -m ttkit_clean --domain mailtm --no-activate --no-bind-phone -v

# Using Frida MSSDK for real signing
python3 -m ttkit_clean --frida --domain mailtm -v

# Follow a specific user
python3 -m ttkit_clean --follow --email=user@mail.tm --target=username -v
Error Code Handling
| Error 7 | Session/proxy block - automatic switching |
| Error 3053 | Number rejected - try different geographic region |
| Error 3052 | Risky account - automatic cooldown |
| Error 3002284 | Profile edit limit - backoff 10-40 minutes |
| Error 0 | Success — continue the pipeline |
| Error 10 | Signature verification failed — resign and check clock / ts |
| Error 1105 | Captcha required — stop or rotate device/proxy |
| Error 2046 | Password / XOR encoding mismatch — retry with 0x05 or 0x17 |
| Error 2048 | Account not found — verify username before continuing |
| Error 2096 | OTP send rate limit — wait 60s and change IP |
What's Included
- Complete source code - All Python files + SignServer JAR
- Runtime data - proxies.txt, sessions, configurations
- Direct technical support from developer
- Free lifetime updates
- Money-back guarantee if not working
Why ttkit_clean?
- Original Developer: Team specialized in TikTok algorithms for 4+ years
- Tested and Proven: Over 50 million accounts created
- Global Clients: 800+ customers across 65 countries
- Instant Updates: Rapid response to any TikTok updates
Contact Information
Telegram: @xsofa | WhatsApp: +20 100 199 5914 | Email: info@strong-pnd.com
Important GitHub Notice
The link below leads to a demo/documentation version of the project. The paid version contains additional features and updated code.
View Demo VersionKey Features
High productivity reaching 1000+ accounts daily with tested 99.8% success rate
Complete Device Trust Score bypass using advanced circumvention techniques
Intelligent AI behavioral simulation with 99.9% accuracy for natural platform interaction
Sophisticated Anti-Bot Evasion techniques to avoid detection systems
100% authentic device fingerprints for Samsung, OPPO, Xiaomi, Huawei, OnePlus, realme
Military-grade Java SignServer cryptographic server running on Port 8000
Advanced _metasec engine with Argus/Ladon algorithms extracted from Metasec research
Comprehensive email service integration: mail.tm, 1secmail, IMAP protocol
5SIM API integration for phone numbers from 195 countries worldwide
Complete auto-activation including: FYP browsing, likes, profile update, avatar upload
Frida MSSDK bridge for real in-app signing capability (Port 8790)
Multi-threading system for parallel processing of thousands of accounts
Smart proxy management with GeoNode/IPRoyal support and cooldown tracking
JSON session STRONG with full fingerprint recovery capability
Automatic Host Rotation with log16-* servers support
Professional CLI interface supporting: create, onboard, bind-phone, follow commands
Error Recovery system with intelligent backoff mechanism for error handling
Pre-loaded libraries: requests, SignerPy, pycryptodome, gmssl
Full local signing: X-Gorgon, X-Argus, X-Ladon, X-Khronos, X-SS-STUB
MSSDK / libmetasec handling with optional in-app Frida signing path
sig_hash and version_code alignment with Android v44.3.x builds
Domain and cookie warm-up via get_domains/v5 before sensitive steps
Structured handling of Captcha (1105), pre_check, and region hashed_id
Passport XOR body encoding (0x05 / 0x17) for login-related flows